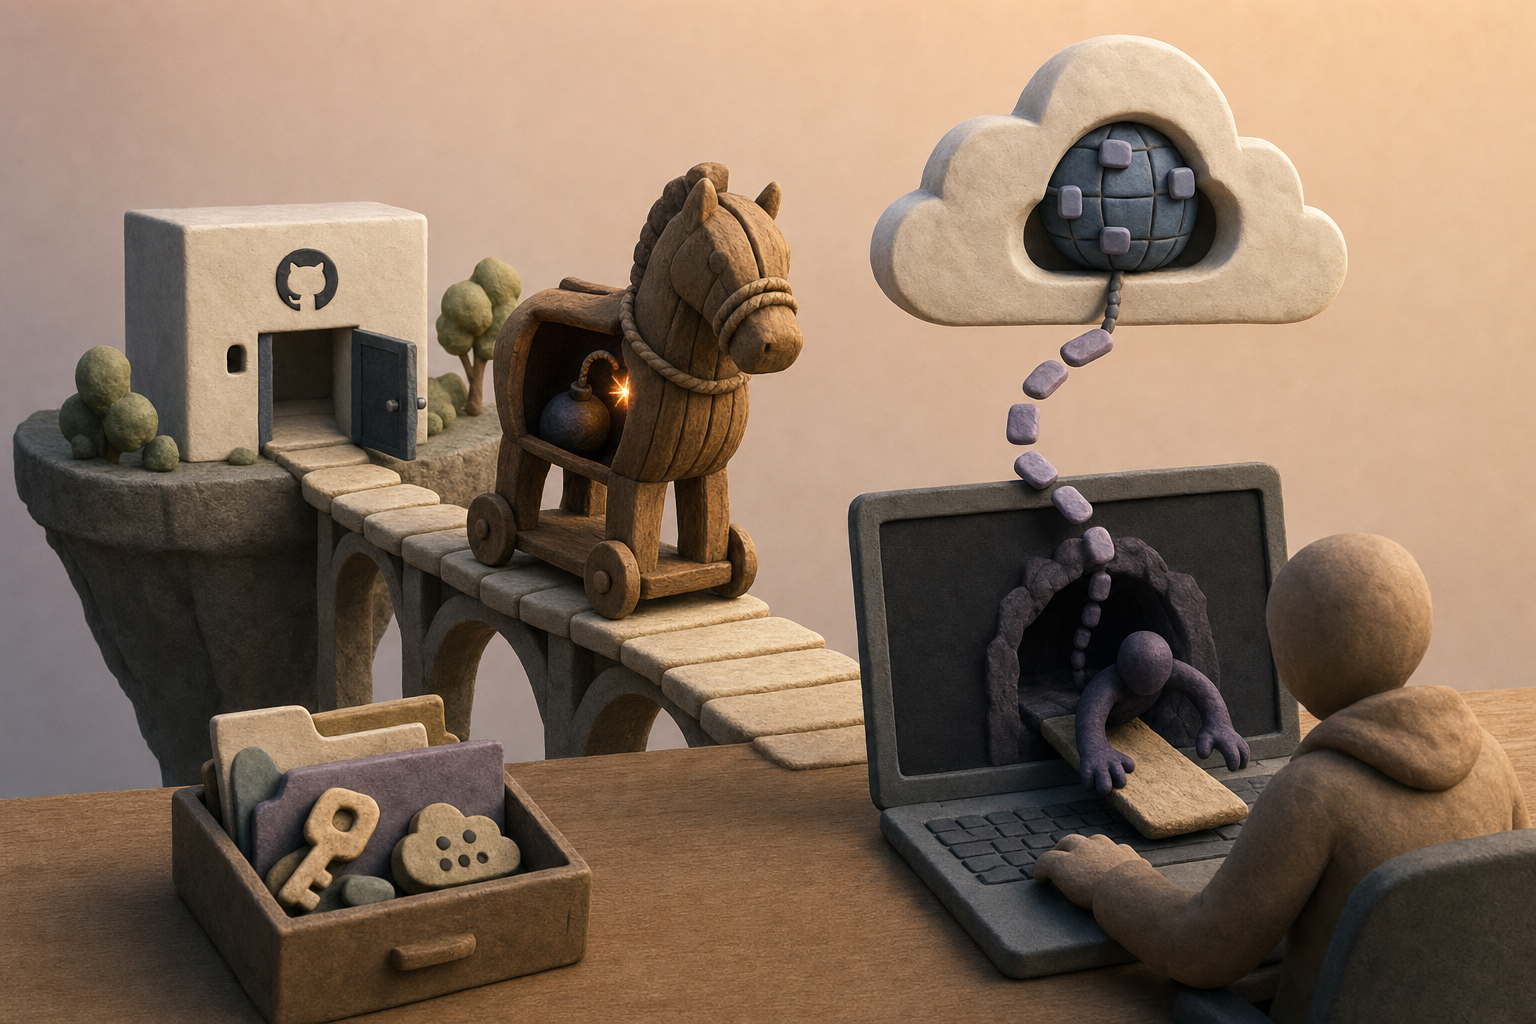
Researchers at Mozilla's AI security platform 0DIN (Zero Day Investigative Network) have demonstrated an attack that uses a "clean" GitHub repository containing no malicious code to make Anthropic's AI coding agent Claude Code launch a reverse shell on a developer's machine. Reported on June 27, 2026, the technique is a proof of concept that manipulates the agent through indirect prompt injection, with no large-scale real-world damage reported so far.
Continue reading
The rest of this article is for AI News Blitz readers. Choose an option below to keep reading.
Already purchased? Sign in✓ Signed in — this article isn’t included in your current plan.
Unlocking the full article...
Contact us
Questions, corrections, or ideas? Send us a message here. We aim to reply by email within 24 hours.
Thank you. Your message has been sent. We aim to reply by email within 24 hours.Please enter your email address and a message.We could not send your message. Please try again in a little while.