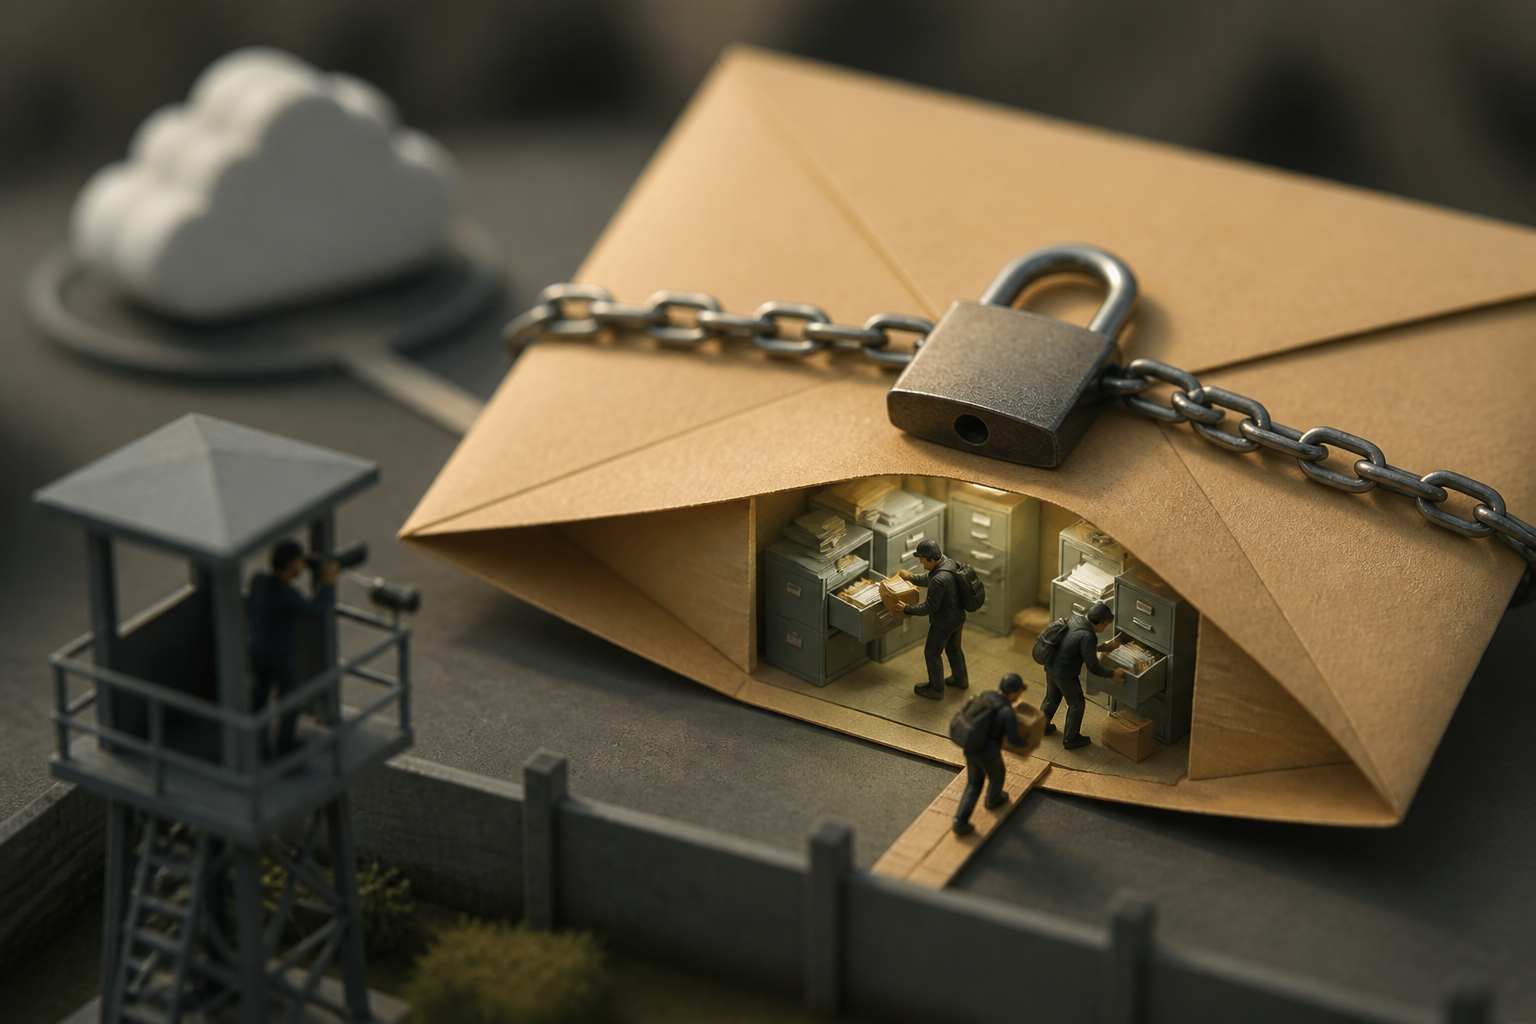
A newly published analysis argues that conventional Secure Access Service Edge (SASE) architectures have a critical blind spot: they can verify an encrypted connection to a large language model, but cannot inspect the intent of what an AI agent is doing inside that connection. The core concern is that an autonomous agent can invoke Model Context Protocol (MCP) tools to pull proprietary code or internal documents while a cloud proxy sees only valid, encrypted HTTPS traffic passing through.
Continue reading
The rest of this article is for AI News Blitz readers. Choose an option below to keep reading.
Already purchased? Sign in✓ Signed in — this article isn’t included in your current plan.
Unlocking the full article...
Contact us
Questions, corrections, or ideas? Send us a message here. We aim to reply by email within 24 hours.
Thank you. Your message has been sent. We aim to reply by email within 24 hours.Please enter your email address and a message.We could not send your message. Please try again in a little while.