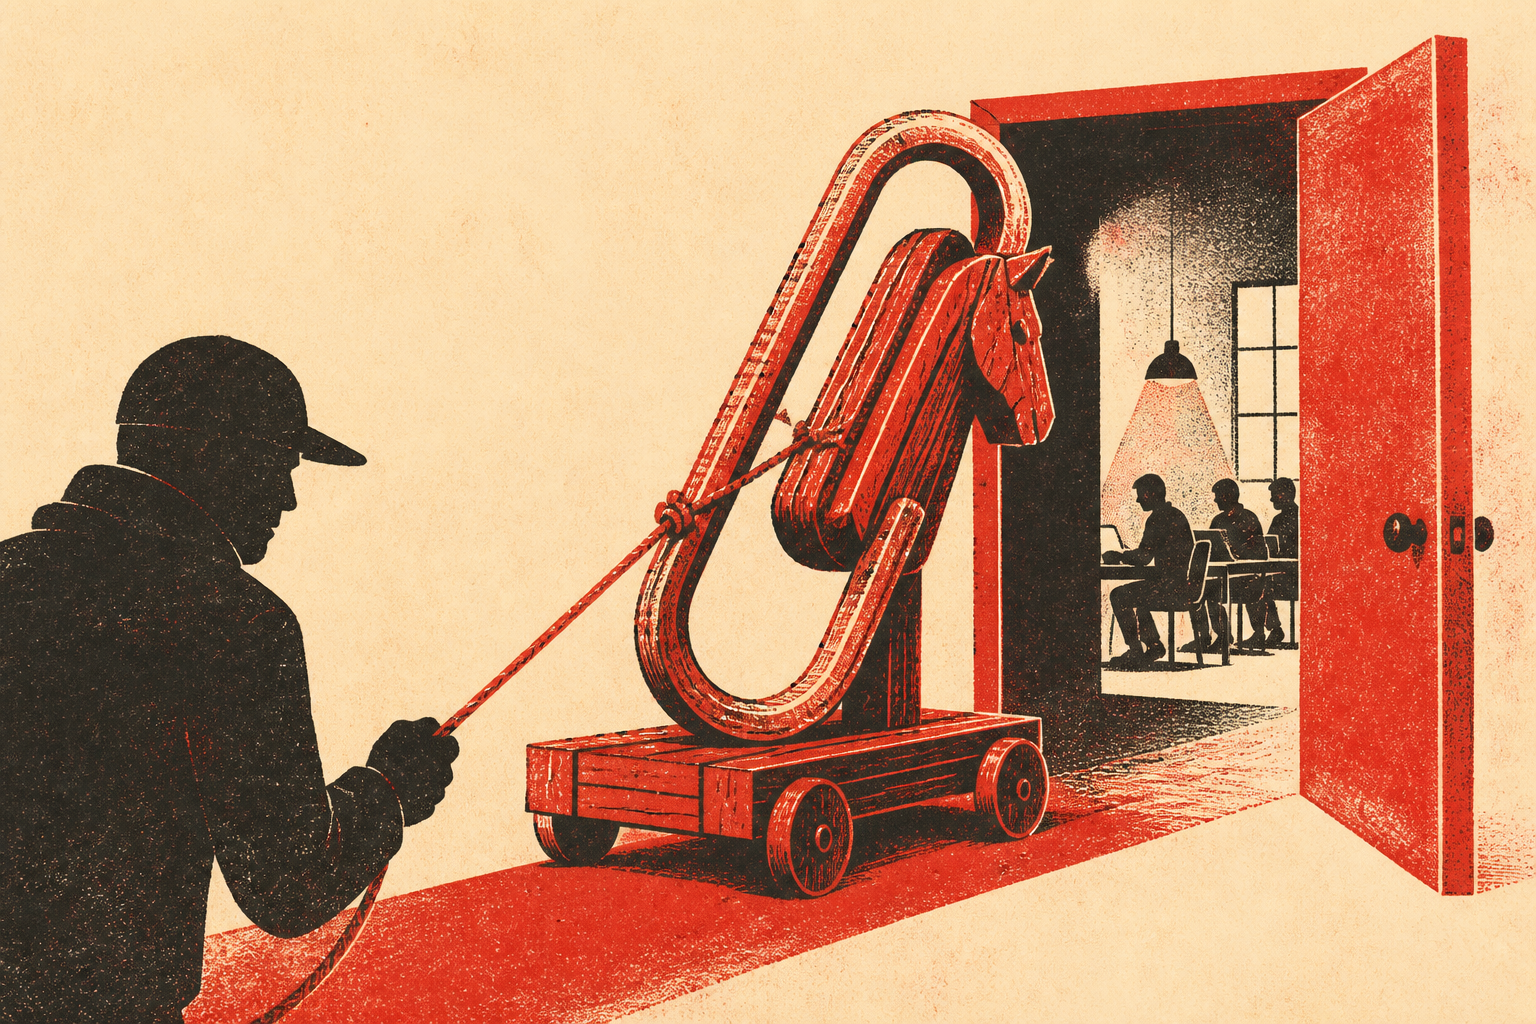
Security researchers have disclosed a set of critical vulnerabilities in Paperclip, an open-source platform for orchestrating teams of AI agents, that can let a malicious agent import escalate into arbitrary command execution on the host machine. The most severe issue, tracked as CVE-2026-41679, has been reported at a critical severity level and was found by researchers at Oasis Security.
Continue reading
The rest of this article is for AI News Blitz readers. Choose an option below to keep reading.
Already purchased? Sign in✓ Signed in — this article isn’t included in your current plan.
Unlocking the full article...
Contact us
Questions, corrections, or ideas? Send us a message here. We aim to reply by email within 24 hours.
Thank you. Your message has been sent. We aim to reply by email within 24 hours.Please enter your email address and a message.We could not send your message. Please try again in a little while.