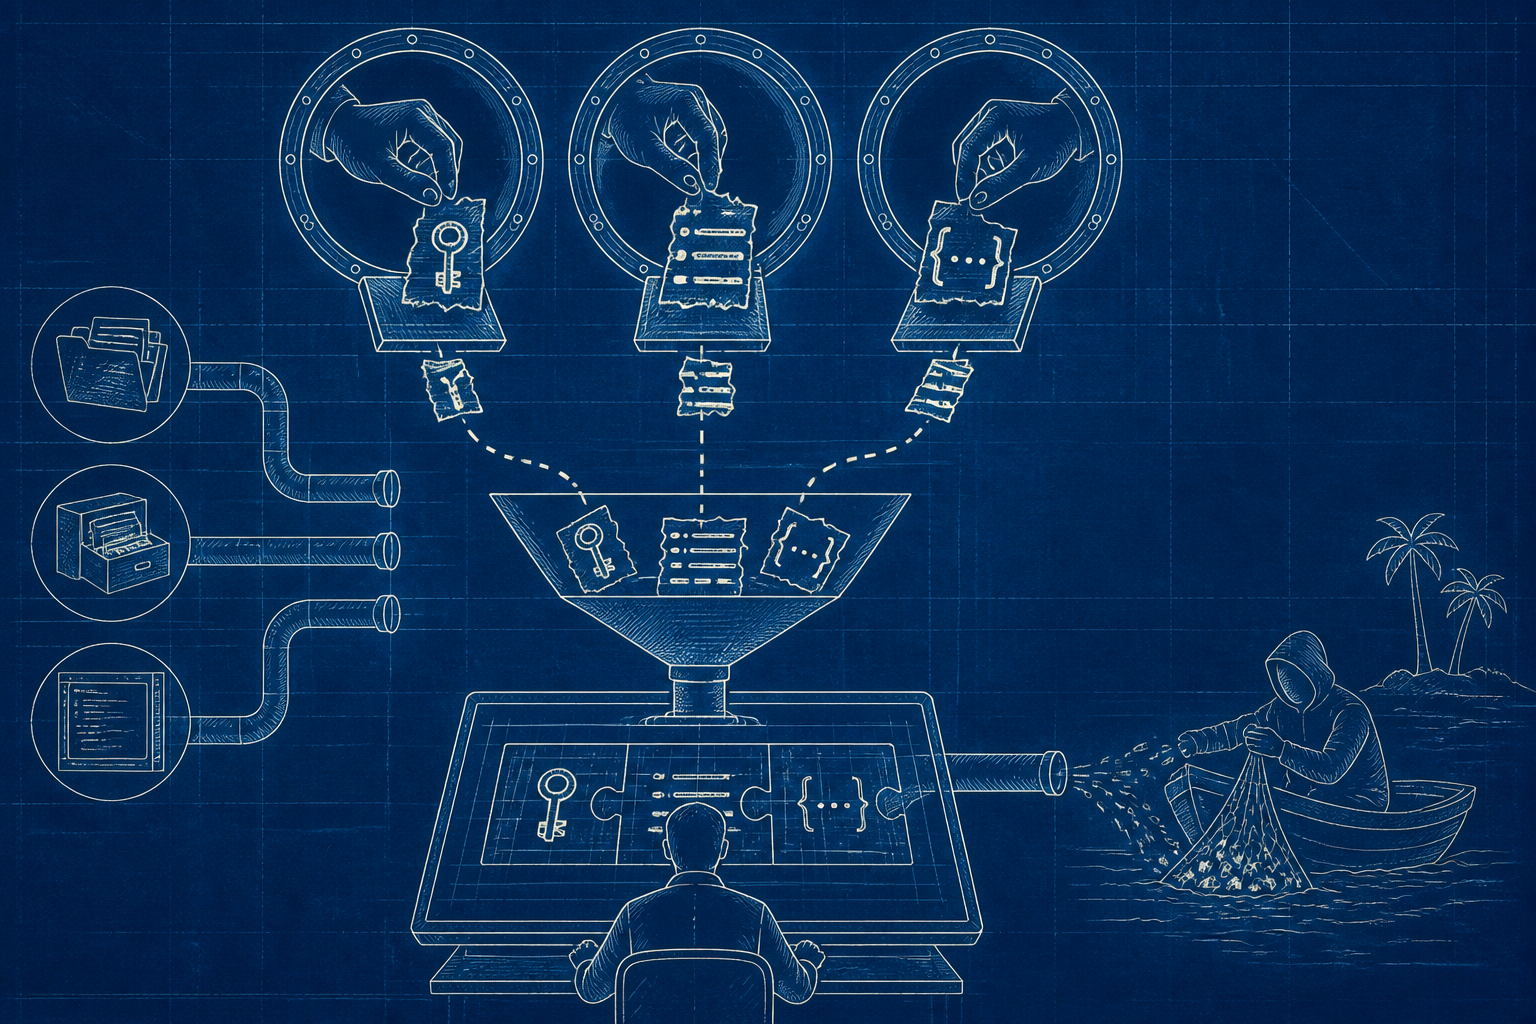
Security researchers have disclosed a new attack technique, dubbed "GhostSplice," that can coax AI coding agents into exfiltrating SSH keys, .env secrets, source code, and customer data by routing malicious instructions through rogue Model Context Protocol (MCP) servers. The method fragments a single malicious request across multiple MCP channels so that no individual piece looks overtly harmful, defeating safety checks that inspect content in isolation.
Continue reading
The rest of this article is for AI News Blitz readers. Choose an option below to keep reading.
Already purchased? Sign in✓ Signed in — this article isn’t included in your current plan.
Unlocking the full article...
Contact us
Questions, corrections, or ideas? Send us a message here. We aim to reply by email within 24 hours.
Thank you. Your message has been sent. We aim to reply by email within 24 hours.Please enter your email address and a message.We could not send your message. Please try again in a little while.