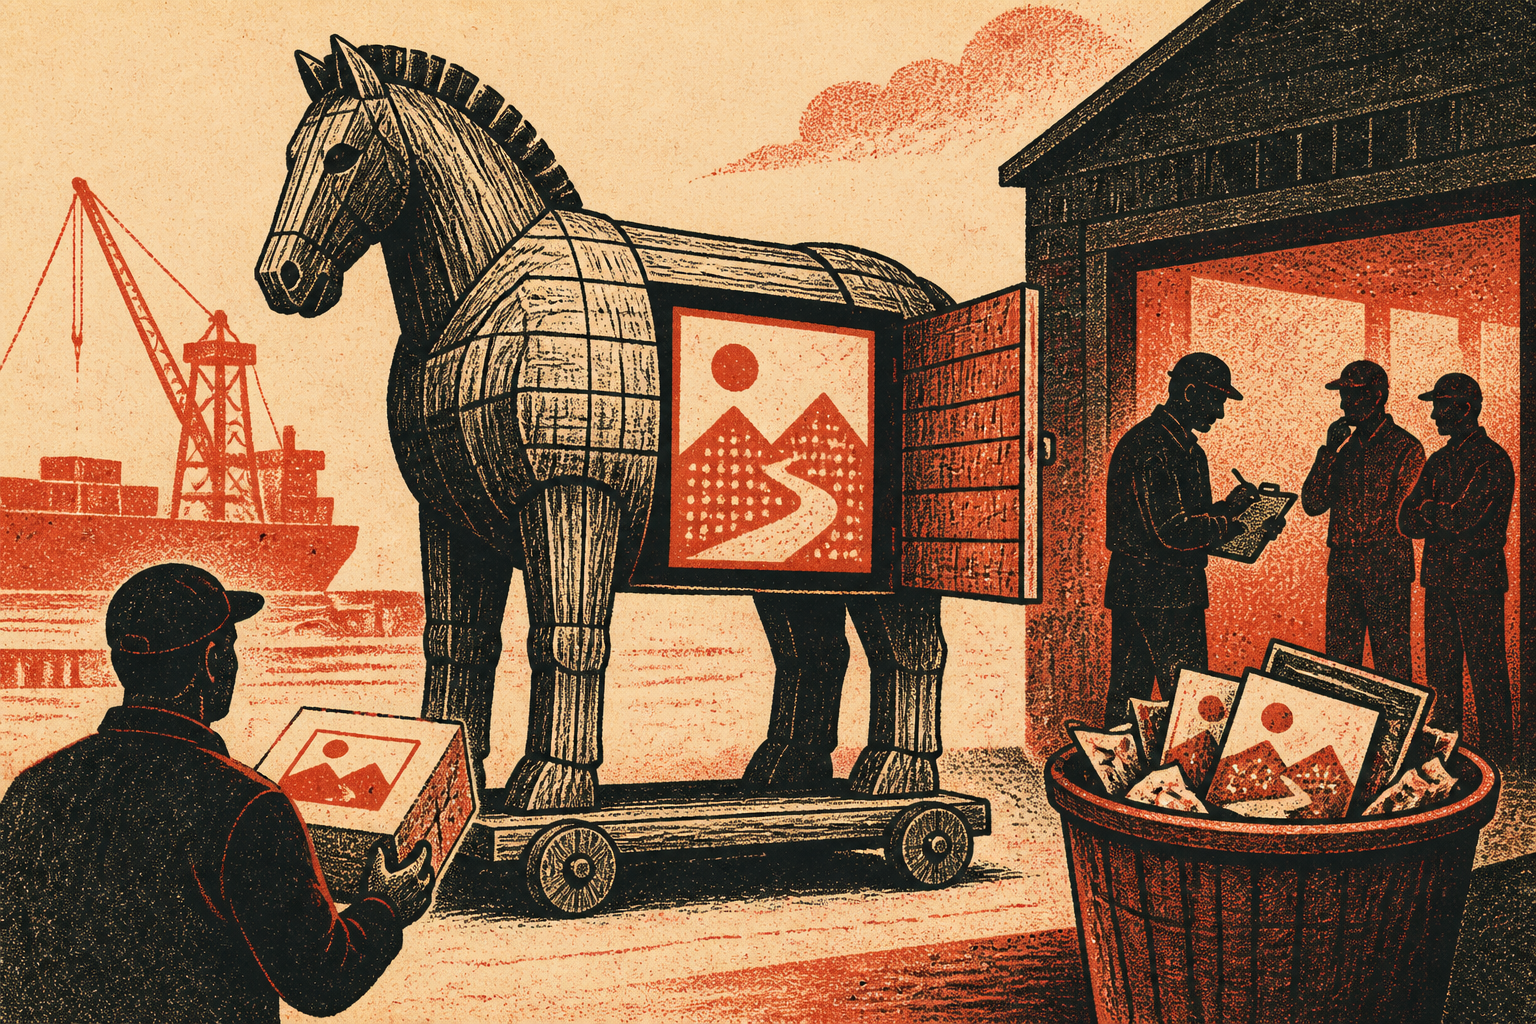
Security researchers have disclosed a new supply-chain attack called "Ghostcommit" that smuggles prompt-injection instructions inside PNG images, slipping past AI code reviewers and tricking coding agents into leaking a repository's secrets. The technique, published on July 11, 2026, as a proof-of-concept by the ASSET Research Group at the University of Missouri-Kansas City, exposes a blind spot in how automated review tools and coding assistants handle non-text files.
Continue reading
The rest of this article is for AI News Blitz readers. Choose an option below to keep reading.
Already purchased? Sign in✓ Signed in — this article isn’t included in your current plan.
Unlocking the full article...
Contact us
Questions, corrections, or ideas? Send us a message here. We aim to reply by email within 24 hours.
Thank you. Your message has been sent. We aim to reply by email within 24 hours.Please enter your email address and a message.We could not send your message. Please try again in a little while.